OC10.0.10 ldap integration and users sync

Steps to reproduce

  1. Install OwnCloud server 10.0.10
  2. Add App LDAP Integration 0.12.0
  3. Run:
    sudo -u apache php occ user:sync “OCA\User_LDAP\User_Proxy”
    But have gotten only 459 users instead 46000
  4. Then I have increased type of data in database “character varying(512)” instead “character varying(255)” oc_ldap_user_mapping COLUMN ldap_dn
  5. After that I have get all 46K users. Auth is working.
  6. Daily I run for sync by cron
    sudo -u apache php occ user:sync “OCA\User_LDAP\User_Proxy” -m disable -r -c -vvv

Expected behaviour

All disabled users in AD will be disabled in OC
All re-enabled users in AD will be re-enabled in OC

Actual behaviour

Several users have been disabled in OC but some of enabled in AD.
A lot of users disabled in AD but enabled in OC

Server configuration

Operating system: RHEL 7.6

Web server: Apache/2.4.6

Database: psql (PostgreSQL) 9.6.11

PHP version: PHP 7.2.12

ownCloud version: 10.0.10 (stable)

List of activated apps:

Enabled:
  - comments: 0.3.0
  - configreport: 0.1.1
  - dav: 0.4.0
  - federatedfilesharing: 0.3.1
  - federation: 0.1.0
  - files: 1.5.1
  - files_external: 0.7.1
  - files_sharing: 0.11.0
  - files_trashbin: 0.9.1
  - files_versions: 1.3.0
  - files_videoplayer: 0.9.8
  - firstrunwizard: 1.1
  - market: 0.2.5
  - notifications: 0.3.5
  - provisioning_api: 0.5.0
  - systemtags: 0.3.0
  - updatenotification: 0.2.1
  - user_ldap: 0.12.0
Disabled:
  - encryption
  - external
  - user_external

Are you using an external user-backend, if yes which one: ActiveDirectory

LDAP configuration (delete this part if not used)

+-------------------------------+---------------------------------------------------------------------------------------------------------------------------------------+
| Configuration                 |                                                                                                                                       |
+-------------------------------+---------------------------------------------------------------------------------------------------------------------------------------+
| hasMemberOfFilterSupport      | 1                                                                                                                                     |
| hasPagedResultSupport         |                                                                                                                                       |
| homeFolderNamingRule          |                                                                                                                                       |
| lastJpegPhotoLookup           | 0                                                                                                                                     |
| ldapAgentName                 | CN=user,OU=ServiceAcc,OU=service,DC=dp,DC=*****,DC=**                                                                               |
| ldapAgentPassword             | ***                                                                                                                                   |
| ldapAttributesForGroupSearch  |                                                                                                                                       |
| ldapAttributesForUserSearch   |                                                                                                                                       |
| ldapBackupHost                |                                                                                                                                       |
| ldapBackupPort                |                                                                                                                                       |
| ldapBase                      | DC=dp,DC=*****,DC=**                                                                                                                 |
| ldapBaseGroups                | DC=dp,DC=*****,DC=**                                                                                                               |
| ldapBaseUsers                 | DC=dp,DC=******,DC=**                                                                                                                 |
| ldapCacheTTL                  | 600                                                                                                                                   |
| ldapConfigurationActive       | 1                                                                                                                                     |
| ldapDynamicGroupMemberURL     |                                                                                                                                       |
| ldapEmailAttribute            | mail                                                                                                                                  |
| ldapExperiencedAdmin          | 1                                                                                                                                     |
| ldapExpertUUIDGroupAttr       |                                                                                                                                       |
| ldapExpertUUIDUserAttr        | objectguid                                                                                                                            |
| ldapExpertUsernameAttr        |                                                                                                                                       |
| ldapGroupDisplayName          | cn                                                                                                                                    |
| ldapGroupFilter               | (|(cn=Domain Users)(cn=********))                                                                                                 |
| ldapGroupFilterGroups         | Domain Users;**********                                                                                                             |
| ldapGroupFilterMode           | 0                                                                                                                                     |
| ldapGroupFilterObjectclass    |                                                                                                                                       |
| ldapGroupMemberAssocAttr      | uniqueMember                                                                                                                          |
| ldapHost                      | ******                                                                                                                            |
| ldapIgnoreNamingRules         |                                                                                                                                       |
| ldapLoginFilter               | (&(&(|(objectclass=person))(|(|(memberof=CN=Domain Users,CN=Users,DC=dp,DC=*****,DC=**)(primaryGroupID=513))))(samaccountname=%uid)) |
| ldapLoginFilterAttributes     |                                                                                                                                       |
| ldapLoginFilterEmail          | 0                                                                                                                                     |
| ldapLoginFilterMode           | 1                                                                                                                                     |
| ldapLoginFilterUsername       | 1                                                                                                                                     |
| ldapNestedGroups              | 0                                                                                                                                     |
| ldapOverrideMainServer        |                                                                                                                                       |
| ldapPagingSize                | 1000                                                                                                                                  |
| ldapPort                      | 389                                                                                                                                   |
| ldapQuotaAttribute            |                                                                                                                                       |
| ldapQuotaDefault              |                                                                                                                                       |
| ldapTLS                       | 0                                                                                                                                     |
| ldapUserDisplayName           | displayName                                                                                                                           |
| ldapUserDisplayName2          |                                                                                                                                       |
| ldapUserFilter                | (&(|(objectclass=person))(|(|(memberof=CN=Domain Users,CN=Users,DC=dp,DC=*****,DC=**)(primaryGroupID=513))))                         |
| ldapUserFilterGroups          | Domain Users                                                                                                                          |
| ldapUserFilterMode            | 0                                                                                                                                     |
| ldapUserFilterObjectclass     | person                                                                                                                                |
| ldapUserName                  | samaccountname                                                                                                                        |
| ldapUuidGroupAttribute        | auto                                                                                                                                  |
| ldapUuidUserAttribute         | auto                                                                                                                                  |
| turnOffCertCheck              | 1                                                                                                                                     |
| useMemberOfToDetectMembership | 1                                                                                                                                     |
+-------------------------------+---------------------------------------------------------------------------------------------------------------------------------------+

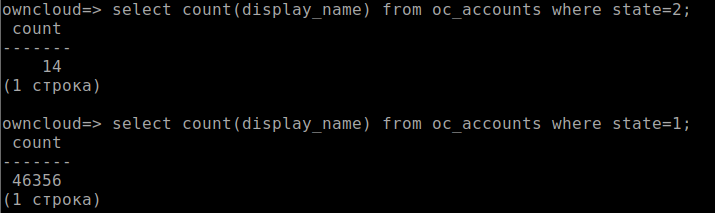
You have 46k users and no support subscription? :slight_smile:

What happens if you run the command without the -r option?

Are all the users. who are disabled in AD also disabled in oC?

Not all 46K users from AD are using oC. We have something about 1200 active users in oC.
If I run the command without the -r option I get several disabled users in oC, but they is not disabled in AD!
All the users. who are disabled in AD are not disabled in oC.

How is it works?) I don’t understand(

There is an LDAP filter that looks for exactly that attribute, “disabled in AD” but I don’t remember.

You can google it and play around with the LDAP filter.

Thank you so much, Dmitry! I found it. I have added !(userAccountControl:1.2.840.113556.1.4.803:=2) in my ldap request. Now it works properly. You have shown me right way! :slightly_smiling_face:

ldapUserFilter:

(&(|(objectclass=organizationalPerson))(!(userAccountControl:1.2.840.113556.1.4.803:=2))(|(|(memberof=CN=Domain Users,CN=Users,DC=dp,DC=mosreg,DC=ru)(primaryGroupID=513))))

Yay :wink:

I am glad that you got it working and thanks for sharing the filter with us.

I am sure your work will help many other who run in the same issue as you.